Cyber Recovery vs. Disaster Recovery: Understanding the Difference
October 13, 2026
From Compliance to Continuous Security: The Changing GCC Cybersecurity Model
October 27, 2026Corporate credentials on the dark web can expose organizations to serious risks. Learn how monitoring and threat intelligence help prevent compromise.
Introduction
Usernames and passwords remain one of the most valuable assets for cybercriminals. Modern attackers no longer rely solely on malware or technical exploits to gain access to organizations. In many cases, access begins with valid credentials that have been stolen, leaked, purchased, or shared through underground criminal marketplaces.
When corporate credentials appear on the dark web, the risk extends far beyond a single employee account. Exposed credentials can provide attackers with access to cloud services, email platforms, VPNs, remote-access systems, business applications, privileged accounts, and sensitive corporate data.
The dark web has evolved into a large underground economy where threat actors buy and sell stolen information, including usernames, passwords, cookies, session tokens, API keys, remote access credentials, and identity data. Credentials can originate from phishing attacks, malware infections, third-party breaches, credential stuffing attacks, infostealer malware, weak passwords, or previously compromised systems.
For organizations across Qatar, Saudi Arabia, the UAE, Bahrain, Kuwait, and Oman, where digital transformation, cloud adoption, remote access, and interconnected business systems continue to expand, exposed credentials represent a growing cybersecurity challenge.
The key question is no longer:
“Can credentials be exposed?”
It is:
“How quickly can we identify exposed credentials, assess the risk, contain the threat, and prevent attackers from turning stolen identities into a business-impacting incident?”
This is where Dark Web Monitoring, Threat Intelligence, Identity Security, and Continuous Cyber Defense become essential components of a modern security strategy.
Understanding the Dark Web
The internet is commonly divided into three broad layers.
- Surface Web – Publicly accessible websites indexed by search engines.
- Deep Web – Content not indexed by search engines, including internal business systems, cloud applications, databases, and private platforms.
- Dark Web – Hidden services accessible through specialized technologies where cybercriminal marketplaces, forums, and underground communities often exchange stolen information.
It is important to understand that not all dark web activity is malicious. However, many cybercriminal groups use dark web platforms to trade:
- Stolen usernames and passwords
- Corporate email accounts
- Remote access credentials
- VPN accounts
- Cloud identities
- Session cookies
- Authentication tokens
- Financial information
- Source code
- Sensitive documents
- Personally identifiable information (PII)
For attackers, stolen credentials are often easier to exploit than technical vulnerabilities because valid accounts can provide legitimate access without triggering traditional security controls.
How Corporate Credentials End Up on the Dark Web
Corporate credentials can appear on the dark web through several attack methods.
Phishing Attacks: Attackers create fraudulent emails, login pages, or messages designed to trick users into revealing usernames and passwords.
Infostealer Malware: Malware installed on employee devices can collect:
- Browser passwords
- Session cookies
- Saved credentials
- Authentication tokens
- Cryptocurrency wallets
- Browser history
Modern infostealer malware has become one of the largest sources of leaked credentials.
Third-Party Breaches: An employee may reuse corporate passwords across multiple platforms. If another service is compromised, attackers can use those credentials against enterprise systems.
Credential Stuffing: Threat actors automatically test previously leaked credentials against:
- Microsoft 365
- Google Workspace
- VPN gateways
- Cloud applications
- Remote desktop services
- Enterprise portals
Insider Threats: Employees, contractors, or third parties with access to sensitive information may intentionally or unintentionally expose credentials.
Data Breaches: A successful attack against an organization can expose thousands of user accounts, which may later appear in criminal marketplaces.
What Happens After Credentials Are Exposed?
Finding credentials on the dark web does not automatically mean a compromise has occurred.
However, exposed credentials create an opportunity for attackers.
The attack process often follows a predictable path:
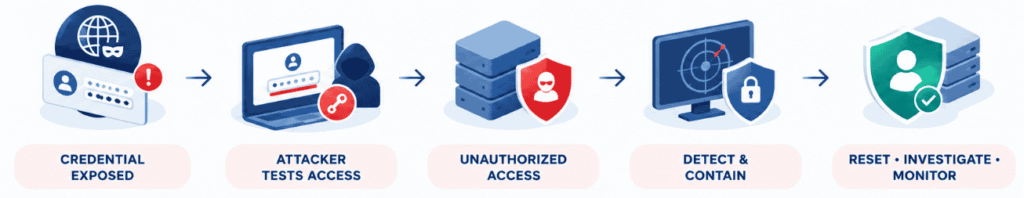
Attackers frequently begin by validating whether exposed credentials remain active.
If successful, they may:
- Access email accounts
- Compromise cloud services
- Connect through VPNs
- Bypass security controls
- Steal additional credentials
- Escalate privileges
- Move laterally
- Access sensitive data
- Deploy ransomware
- Disrupt operations
This demonstrates why exposed credentials should be treated as an early warning indicator rather than simply an information leak.
Why Identity Has Become a Primary Attack Target
Modern organizations increasingly depend on identities rather than traditional network perimeters.
Employees access:
- Cloud applications
- SaaS platforms
- Remote systems
- APIs
- Mobile applications
- Third-party environments
- Hybrid infrastructures
As a result, identities have become one of the most important security layers.
A compromised identity can potentially provide attackers with legitimate access that bypasses traditional network defenses.
This explains why many modern attacks focus on:
- User accounts
- Privileged accounts
- Service accounts
- Authentication systems
- Remote access services
- Cloud identities
Identity protection therefore requires more than password policies alone.
Organizations increasingly require:
- Multi-Factor Authentication (MFA)
- Conditional Access
- Privileged Access Management (PAM)
- Identity Threat Detection & Response (ITDR)
- Dark Web Monitoring
- User Behavior Analytics
- Continuous Authentication Monitoring
The Importance of Dark Web Monitoring
Organizations cannot protect credentials they do not know have been exposed.
Dark web monitoring helps organizations identify:
- Exposed email addresses
- Leaked passwords
- Compromised accounts
- Threat actor activity
- Third-party exposure
- Credential reuse risks
- Emerging attack campaigns
Early visibility allows organizations to:
- Reset passwords
- Disable accounts
- Enforce MFA
- Investigate suspicious activity
- Review access permissions
- Increase monitoring
The objective is not simply to discover leaked credentials.
It is to reduce the amount of time attackers have to exploit them.
Dark Web Monitoring and Threat Intelligence
Dark web monitoring becomes more effective when combined with threat intelligence.
Threat intelligence adds context, including:
- Threat actor behavior
- Attack campaigns
- Malware families
- Credential marketplaces
- Indicators of compromise
- Emerging attack methods
This allows organizations to move from:
“Credentials were exposed.”
To:
“Which threat groups may be using them, what systems are at risk, and what actions should we take?”
This transition from data collection to actionable intelligence significantly improves security decision-making.
The Role of Continuous Monitoring
Credential exposure can occur at any time.
An attacker may attempt access:
- During weekends
- Outside business hours
- During holidays
- During migration projects
- During large business events
This makes continuous monitoring essential.
A modern Cyber Defense Center (SOC) provides:
- 24/7 visibility
- Identity monitoring
- Endpoint monitoring
- Network monitoring
- Threat correlation
- Investigation
- Incident response
CORVIT’s Cyber Defense Center combines continuous monitoring, threat intelligence, behavioral analytics, and expert investigation to identify suspicious activity associated with compromised identities.
How CORVIT MSSP Helps Reduce Credential Risks
CORVIT MSSP approaches identity security as part of a broader cybersecurity lifecycle:
Access → Govern → Protect → Detect → Respond → Recover → Evolve
CORVIT capabilities supporting credential-related threats include:
24/7 Cyber Defense Center: Continuous monitoring, threat detection, and incident response.
Threat Intelligence: Visibility into emerging threats, attacker activity, and credential exposure.
Threat Hunting: Proactive investigation of suspicious identity-related activity.
EDR/XDR: Endpoint visibility and automated response capabilities.
AI-Driven NDR: Network monitoring to identify unusual access patterns.
Managed Firewall & IPS: Protection against malicious traffic and unauthorized access.
Identity Security: Support for identity monitoring, authentication protection, and identity-based threat detection.
Together, these capabilities help organizations reduce exposure, improve visibility, and respond quickly when credentials become compromised.
A Practical Response to Exposed Credentials
When corporate credentials appear on the dark web, organizations should:
- Verify the exposure.
- Reset affected passwords.
- Enable MFA.
- Review privileged accounts.
- Investigate authentication logs.
- Monitor suspicious activity.
- Search for attacker persistence.
- Assess third-party exposure.
- Review identity controls.
- Strengthen ongoing monitoring.
The faster these actions occur, the lower the likelihood that attackers can convert exposed credentials into a larger compromise.
Conclusion
Corporate credentials appearing on the dark web should not be viewed as an isolated security event.
They should be treated as an indicator that identities, systems, users, or third-party environments may be exposed to additional risk.
The challenge is not only preventing credential theft. It is identifying exposure quickly, understanding the risk, monitoring for suspicious activity, and responding before attackers establish access.
Stolen credentials create opportunity. Continuous cyber defense determines how far attackers can go.
CORVIT MSSP combines 24/7 Cyber Defense, Threat Intelligence, Threat Hunting, EDR/XDR, AI-Driven NDR, Managed Firewall/IPS, Identity Security, and Incident Response capabilities to help organizations identify credential exposure, strengthen identity protection, and reduce cyber risk.
Explore CORVIT MSSP: https://corvit.com/networks/mssp/
FAQs
1- What does it mean if corporate credentials appear on the dark web?
It means usernames, passwords, or identity-related information associated with the organization have been exposed, leaked, or offered in underground forums or marketplaces.
2- Does exposed credentials mean the organization has been breached?
Not necessarily. However, exposed credentials increase the risk of unauthorized access and should be investigated promptly.
3- How do credentials reach the dark web?
Common causes include phishing, malware, credential reuse, third-party breaches, insider threats, and infostealer malware.
4- Why is MFA important?
MFA provides an additional layer of security, reducing the likelihood that stolen passwords alone can be used for unauthorized access.
5- How does dark web monitoring help?
Dark web monitoring helps organizations identify exposed credentials early, enabling faster response and reducing attacker opportunities.